Exposed secrets in code represent a growing threat: in 2024 alone, 23 million hardcoded secrets were detected on GitHub, and any public key can become a gateway to sensitive data and critical services
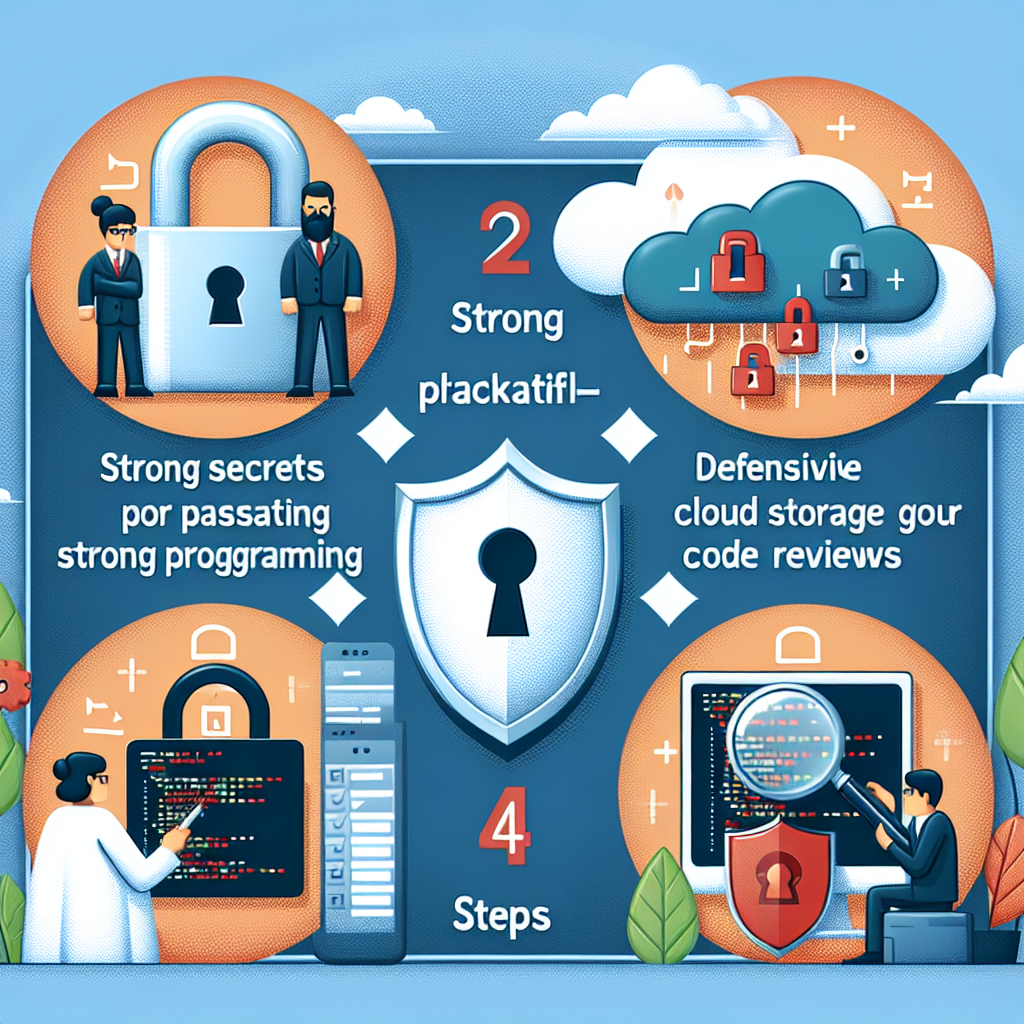
Step 1 Classify by sensitivity to prioritize response Identify administrator credentials, production certificates, and payment keys as high priority compared to test keys or low-sensitivity examples Applying risk labels helps focus efforts on what can actually cause harm
Step 2 Assess scope and impact Determine whether the secret is public, in which repositories it appears, and which systems or accounts it affects Analyze associated permissions, exposed environments, and potential exploitation paths to estimate impact and urgency
Step 3 Identify root causes to prevent recurrence Review commit history and review practices Detect frequent errors such as careless commits, missing CI hooks, or lack of training in good security practices and correct them with clear, automated policies
Step 4 Enrich with metadata and operational controls Assign ownership, access levels, and expiration dates to each secret Implement rotation policies, just-in-time access, and continuous auditing to reduce the exposure window
Open tools and recommended practices Integrate automatic detectors such as TruffleHog and git-secrets into CI pipelines SOPS and HashiCorp Vault facilitate encryption, management, and secure provisioning of secrets Add continuous scanning, alerts, and remediation playbooks for rapid responses
Prevention in the development lifecycle Combine code reviews, pre-commit hooks, pipeline scanning, and ongoing developer training Establish regular key rotation, time-limited access, and granular permission control in cloud services
How Q2BSTUDIO handles exposed secrets Q2BSTUDIO is a custom software and application development company specialized in artificial intelligence and cybersecurity We offer comprehensive solutions including risk assessment, integration of tools such as TruffleHog and HashiCorp Vault, key rotation automation, and access policy design for AWS and Azure cloud environments
Our services include custom software development, custom applications, business intelligence services, Power BI implementations, AI solutions for businesses, and AI agents to automate critical tasks We combine cybersecurity expertise with DevSecOps practices to reduce the likelihood of leaks and improve operational resilience
Quick recommendation Implement sensitivity classification, automatic scanning on every commit, metadata enrichment, and just-in-time access controls If you need help auditing repositories, integrating open source tools, or deploying managed vaults, the Q2BSTUDIO team can design and implement a complete secret protection strategy
Keywords for positioning custom applications custom software artificial intelligence cybersecurity AWS and Azure cloud services business intelligence services AI for businesses AI agents Power BI