In today's computing ecosystem, few elements go as unnoticed as secure boot certificates. However, their expiration can become an open door for threats that compromise the integrity of the operating system. We are referring to the Secure Boot certificates originally issued in 2011, whose validity period expires during 2026. If your computer has not yet received the corresponding updates, the risk of infections by bootkits and low-level malware increases significantly. To understand the scope, it is worth remembering that Secure Boot acts as a trust filter in the initial phase of startup: it verifies that each driver, firmware, or loaded component has a valid digital signature, preventing the execution of unauthorized code before the operating system takes control. When those certificates lose their validity, the verification mechanism becomes outdated and, although the PC continues to boot without apparent problems, the real protection weakens.
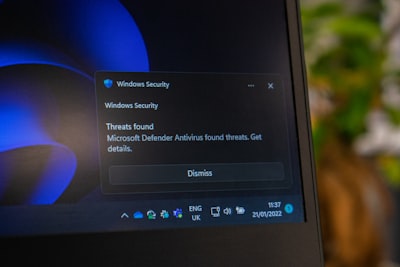
Detecting whether your computer is in this situation is relatively simple. Windows itself shows a notification in the notification area (system tray) via a blue shield icon with a yellow or red marker. Additionally, by accessing the Windows Security app, in the Device security section, we can see the status of secure boot. A green checkmark indicates that the certificates are up to date; any other signal requires user intervention. Many computers, especially those assembled by major manufacturers such as Dell, Lenovo, or HP, automatically received the update to the 2023 certificates, but other older models or custom configurations may have been left behind.
The first measure in the face of such a warning is to update the UEFI/BIOS firmware of the motherboard. Microsoft distributes the new certificates through system updates, but these can only be applied if the computer's firmware is recent enough. For pre-built computers, the most effective approach is to go to the manufacturer's support site, where they usually offer automatic diagnostic tools that identify the exact firmware version and guide the update process. In the case of self-assembled systems (DIY), it is essential to know the exact model of the motherboard —including its revision— and download the updates from the manufacturer's page. There, it is advisable to review the version notes to confirm whether the Secure Boot certificate update is included. To avoid problems, it is recommended to proceed gradually: first apply intermediate versions if the firmware is very old, rather than jumping directly to the most recent one.
While waiting for the update, caution in browsing and software management becomes essential. Although the expiration of the certificates does not imply an immediate danger, the time gap leaves the computer exposed to attack vectors that evolve rapidly. It is advisable to be extremely careful with the websites visited, the browser extensions installed, and especially with downloads of applications of dubious origin. Traditional security tools, such as antivirus software, have difficulty detecting bootkits once they are hosted in the boot process, but keeping virus definitions updated helps block the initial installation of malicious code.
The underlying issue is that the ability to receive the new certificates does not depend on Microsoft, but on the hardware manufacturer. If the company that assembled the computer or the motherboard has not published a compatible firmware update, the user faces a dead end. In practice, this usually means that the computer has fallen out of the support cycle and, therefore, is a candidate for a hardware renewal. Some voices suggest migrating to Linux distributions, but many of them also depend on the same certificate ecosystem. Faced with this scenario, the most sensible decision is to plan an orderly transition to a modern computer, thus avoiding exposing data and productivity to unnecessary risks.
From a business perspective, managing the expiration of secure boot certificates should be part of any cybersecurity plan. Organizations that depend on heterogeneous fleets of computers need inventory and monitoring tools that alert about these expirations before they become a vulnerability. This is where the expertise of companies like Q2BSTUDIO becomes relevant: by developing custom applications and custom software for corporate environments, it is possible to integrate firmware and certificate management modules that automate update processes. Furthermore, their cybersecurity solutions include device audits and penetration tests that identify blind spots such as expired certificates. For companies operating in the cloud, the AWS and Azure cloud services offered by Q2BSTUDIO allow centralizing the monitoring of all endpoints, ensuring that each machine complies with updated security policies.
In an environment where artificial intelligence accelerates both the discovery of vulnerabilities and the creation of malware, having AI for businesses that anticipates these risks becomes strategic. The AI agents developed by Q2BSTUDIO can analyze the event logs of computers, detect anomalous behavior patterns during boot, and execute remediations autonomously. Likewise, the Power BI capabilities and business intelligence services they provide allow managers to visualize in real time the health status of the entire fleet of computers, including the validity of secure boot certificates. This comprehensive view not only mitigates risks but also optimizes decision-making regarding hardware renewal and resource allocation.
In short, the expiration of Secure Boot certificates is not a minor alarm. It represents a turning point in the security of any Windows PC, especially when manufacturers stop offering support. The combination of good digital hygiene, timely firmware updates, and the support of specialized technology partners is the recipe for keeping the infrastructure safe. Do not wait for the warning icon to become a real infection: act methodically and, if your fleet of computers requires it, rely on those who understand technology as an interconnected ecosystem, where every certificate, every update, and every cloud service counts to protect the most valuable asset of your organization: information.